Featured
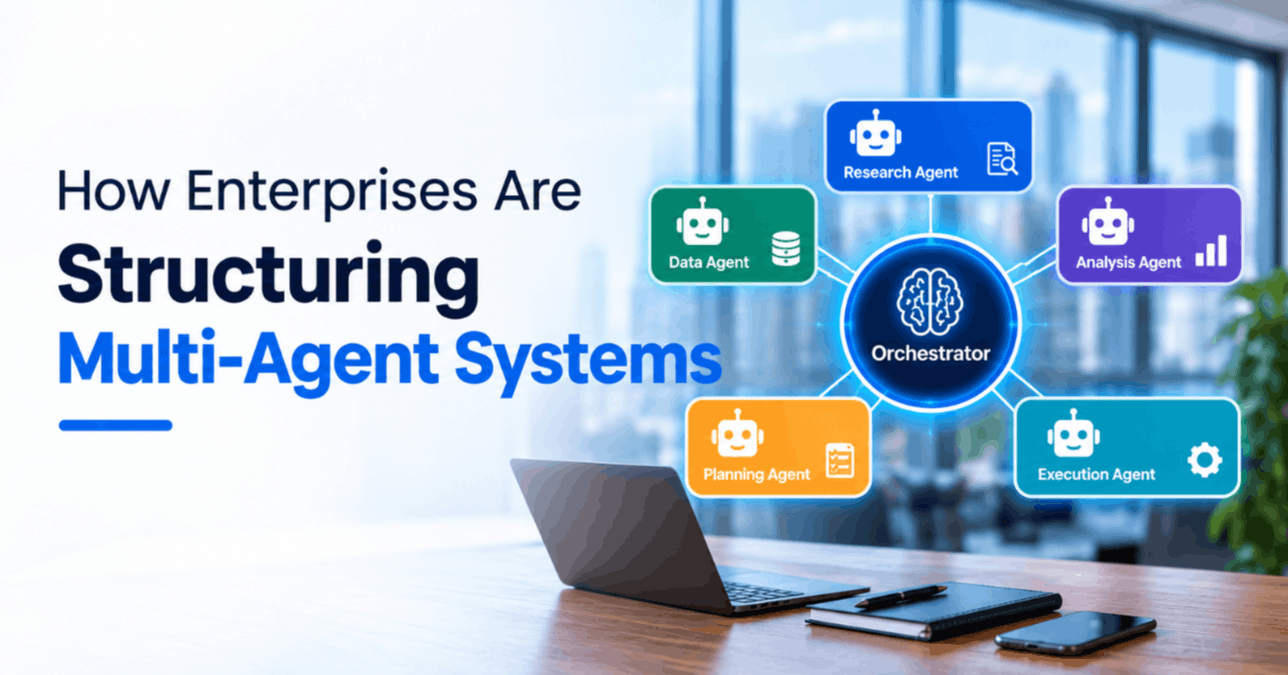
How Enterprises Are Structuring Multi-Agent Systems
The way enterprises deploy AI is changing. Early enterprise AI implementations
were largely single-model systems with one model, one task and one output. That
approach works for contained problems but breaks down quickly when the task
involves multiple steps, multiple data sources or decisions that need to be made
in sequence based on what earlier steps produced. Multi-agent systems are how
enterprises are solving that problem, and the architectural patterns emerging
from early deployments are worth understanding carefully before committing to a
design direction. Key Takeaways * Multi-agent systems distribute complex tasks
across specialized AI agents that collaborate rather than relying on a single
model to do everything. * AI agent orchestration is the coordination layer that
determines how agents communicate, how tasks are routed and how outputs are
passed between agents. * Enterprise AI agent architecture requires deliberate
design around reliability, observability, error handling and security that
single-agent systems do not demand at the same level. * The most successful
enterprise deployments start with a single well-defined workflow and expand the
architecture as operational experience accumulates. What Are Multi-Agent Systems
and Why Do Enterprises Need Them? A multi-agent system is an AI architecture in
which multiple independent AI agents, each with its own capabilities, memory and
decision-making logic, collaborate to complete tasks that would be impractical
or impossible for a single agent to handle reliably. Each agent is specialized
for a particular type of task, and the system as a whole achieves complex
outcomes by coordinating the work of those specialized components. The case for
this approach in enterprise contexts comes down to three practical limitations
of single-agent systems. First, single agents have context window constraints
that make handling long, multi-step workflows unreliable. Second, single agents
perform worse on tasks that require genuinely different capabilities applied in
sequence, because no single model is equally strong across all task types.
Third, single-agent systems are harder to debug, maintain and improve because
every capability is bundled into one system rather than separated into
components that can be evaluated and updated independently. Enterprises dealing
with workflows that span multiple systems, require multiple types of reasoning
or involve long chains of dependent decisions are finding that this architecture
is the practical solution rather than an experimental one. Core Components of
Enterprise AI Agent Architecture Understanding this kind of architecture at the
enterprise level requires understanding the components that every serious
multi-agent system includes. Individual agents are the building blocks. Each
agent has a defined role, access to specific tools or data sources and
instructions that shape how it reasons and acts. An agent might be responsible
for retrieving information from a database, summarizing documents, classifying
inputs, drafting outputs or making routing decisions based on the content it
processes. The orchestration layer is what coordinates agent activity. It
handles task decomposition, which means deciding how an incoming request gets
broken into sub-tasks. It manages task routing, determining which agent handles
which sub-task. It manages state, tracking what has been completed and what
still needs to happen. And it handles communication between agents, passing
outputs from one agent as inputs to the next. In practice, teams typically build
this layer on an established framework rather than from scratch. LangGraph and
CrewAI are common choices for agent-to-agent coordination; AutoGen is often used
for conversational multi-agent setups, and Temporal or similar workflow engines
are frequently brought in when the priority is durable execution and retry
handling across long-running processes. Which framework fits depends heavily on
the workflow's shape, so this is usually one of the first architectural
decisions worth getting right. Memory systems give agents the ability to access
information across the scope of a task. Short-term working memory holds the
context of the current task. Long-term memory stores information that should
persist across sessions. Shared memory makes information available across
multiple agents working on the same workflow simultaneously. Tool integrations
give agents the ability to act, not just reason. APIs, databases, search
systems, code execution environments and external services are all tools that
agents can call to retrieve information, take actions or produce outputs that
are grounded in real data rather than model-generated approximation. How
Enterprises Are Structuring Multi-Agent Systems in Practice The architectural
patterns enterprises are using in production fall into a small number of
recognizable structures, each suited to different workflow characteristics.
Sequential pipelines are the simplest structure. Agent A completes its task and
passes the output to Agent B, which completes its task and passes to Agent C.
This works well for workflows where the steps are clearly defined and the output
of each step is a well-specified input for the next. Document processing
workflows, where a document is classified, then extracted from, then summarized,
then routed, follow this pattern naturally. Supervisor-worker architectures
place an orchestrator agent above a set of worker agents. The orchestrator
receives the task, breaks it into sub-tasks, dispatches those sub-tasks to
appropriate worker agents and assembles the results into a final output. This
pattern handles more complex tasks where the decomposition itself requires
judgment rather than following a fixed sequence. For example, in a logistics
exception-handling workflow, a supervisor agent might receive an alert about a
delayed shipment, then dispatch one worker agent to check carrier tracking data,
another to cross-reference the customer's contract terms for delay penalties and
a third to draft a customer notification. It then assembles those outputs into a
single recommended action for a human operator to approve. Research workflows,
complex customer service escalations and multi-source data synthesis tasks
commonly use this same structure. Parallel processing architectures dispatch
multiple agents to work on different aspects of the same task simultaneously and
aggregate their outputs. When speed is a priority and the sub-tasks are
genuinely independent, this architecture reduces end-to-end latency
significantly compared to sequential approaches. Hierarchical multi-agent
architectures combine supervisor-worker patterns at multiple levels. A top-level
orchestrator coordinates department-level orchestrators, each of which
coordinates a set of specialist agents. Large enterprise deployments where
multiple business functions are automated within the same system frequently
require this level of structural organization. The Design Decisions That
Determine Production Reliability These architectures perform well in design
documentation and controlled testing. What determines whether they perform well
in production is the quality of a set of design decisions that are separate from
the core architecture but directly affect how the system behaves when real
inputs arrive in real volumes. Error handling is the most important of these
decisions. In a multi-agent workflow, an error in one agent can cascade through
subsequent agents in ways that produce incorrect outputs without any obvious
indication that something has gone wrong. Designing explicit error states, retry
logic and fallback behaviors for every agent in the workflow before deployment
is not optional in an enterprise context. Observability is closely related.
Being able to trace exactly what each agent received, what it decided, what it
called and what it produced for any given task execution is essential for
debugging failures, understanding performance degradation and satisfying the
audit requirements that regulated industries impose. Logging and tracing
infrastructure needs to be designed alongside the agent architecture rather than
added after the fact, when a production issue makes its absence apparent.
Security and access control in multi-agent systems requires more careful design
than in single-agent systems, because the attack surface is larger. Each agent
has its own tool access, and each tool integration is a potential vulnerability
if not properly secured. Agent permissions should follow the principle of least
privilege. Each agent should have access only to the tools and data sources it
needs for its defined role and nothing more. Human-in-the-loop design determines
where human oversight is inserted into the workflow. Not every step of a
multi-agent workflow should run autonomously. High-stakes decisions, actions
with significant external consequences and outputs that will be customer-facing
without further review are all candidates for human approval gates within the
automated flow. Where UfaqTech Fits In! UfaqTech is an agentic AI development
company that builds multi-agent systems, AI agent orchestration and LLM-powered
agents for enterprise clients. Our work spans financial planning agents,
autonomous risk analysis and fraud detection in financial services, along with
smart care management and healthcare data processing agents in healthcare. We
focus on connecting agentic AI
smoothly with your existing IT
environment, including data warehouses, databases and business intelligence
applications. Responsible AI is central to how we work. We implement AI
governance frameworks to ensure transparency, reliability and compliance, and
our systems are built for continuous optimisation and performance improvement
over time. With an experienced AI team, UfaqTech supports enterprises building
agentic AI systems at any stage, from early adoption to enterprise-scale
autonomous deployments. Get in touch with our team to discuss your multi-agent
AI project. Final Thoughts Multi-agent AI is not an experimental architecture
anymore. It is the pattern enterprises are using to automate workflows that
single-model systems cannot handle reliably. Getting the architecture right
requires deliberate design across orchestration, memory, tool integration, error
handling, observability and security. All of this needs to be addressed before
the first production workflow goes live, rather than reactively when problems
surface under real operating conditions. The enterprises that invest in that
design work upfront are building AI infrastructure that scales and improves over
time. The ones that skip it are building systems that work in testing and fail
at scale. FAQs 1. What is the difference between a single AI agent and a
multi-agent system? A single AI agent handles a task within one model context
using one set of capabilities and tools. A multi-agent system distributes a
complex task across multiple specialized agents that collaborate, each
contributing a specific capability to the overall workflow. Multi-agent systems
handle longer, more complex tasks more reliably than single agents because the
work is distributed across components optimized for their specific roles. 2.
What is AI agent orchestration and why does it matter? It's the coordination
layer that manages how tasks are decomposed, how sub-tasks are routed to
appropriate agents, how state is tracked across a workflow and how outputs are
passed between agents. Without a well-designed orchestration layer, multi-agent
systems become unpredictable in production because there is no reliable
mechanism for managing the dependencies between agents. 3. How do enterprises
handle errors in multi-agent workflows? Well-designed enterprise multi-agent
systems implement explicit error states, retry logic with configurable backoff,
fallback behaviors that activate when primary agent paths fail and alert systems
that notify human operators when automated error handling is insufficient. The
specific design depends on the workflow and the consequences of different
failure modes. 4. What observability tools are commonly used with enterprise
multi-agent systems? Common approaches include distributed tracing frameworks
that capture agent-level execution detail, centralized logging systems that
aggregate logs across all agents in a workflow, performance monitoring that
tracks latency and throughput at the agent and workflow levels and custom
dashboards that surface the operational metrics most relevant to the business
workflow being automated. 5. How does UfaqTech support enterprise multi-agent
system development? UfaqTech builds multi-agent systems, AI agent orchestration
and LLM-powered agents for enterprise clients, with a focus on financial
services and healthcare use cases. This includes connecting agentic AI
to existing IT environments such as data warehouses, databases and business
intelligence applications, along with AI governance frameworks to ensure
transparency, reliability and compliance.


 and Digital Transformation"
/>